

Your company runs on data. Financial reports. Customer records. Inventory numbers. Forecasts. Compliance logs. Every serious decision pulls from some database somewhere.
Now here’s the uncomfortable part.
What if that data has been quietly altered… and you wouldn’t know?
Most organizations spend heavily on cybersecurity. Firewalls, encryption, endpoint protection, threat monitoring. All important. But those tools focus on keeping people out.
They don’t always answer a simpler, more unsettling question:
Can you prove your data hasn’t been changed?
That’s the real issue. Not theft. Not downtime. But integrity.
And for a lot of enterprises, it’s shakier than they’d like to admit.
What is Data Integrity and the Different Types?
At its core, data integrity just means this: your data stays accurate, complete, and unchanged unless there’s a legitimate, traceable reason for it to change.
It sounds basic. It isn’t.
Think of it like a ship’s log. Every entry reflects what happened, when it happened. If someone can quietly edit those pages later, the whole voyage becomes questionable. You’re not navigating anymore. You’re guessing.
Most companies assume they have data integrity handled. What they usually mean is something narrower.
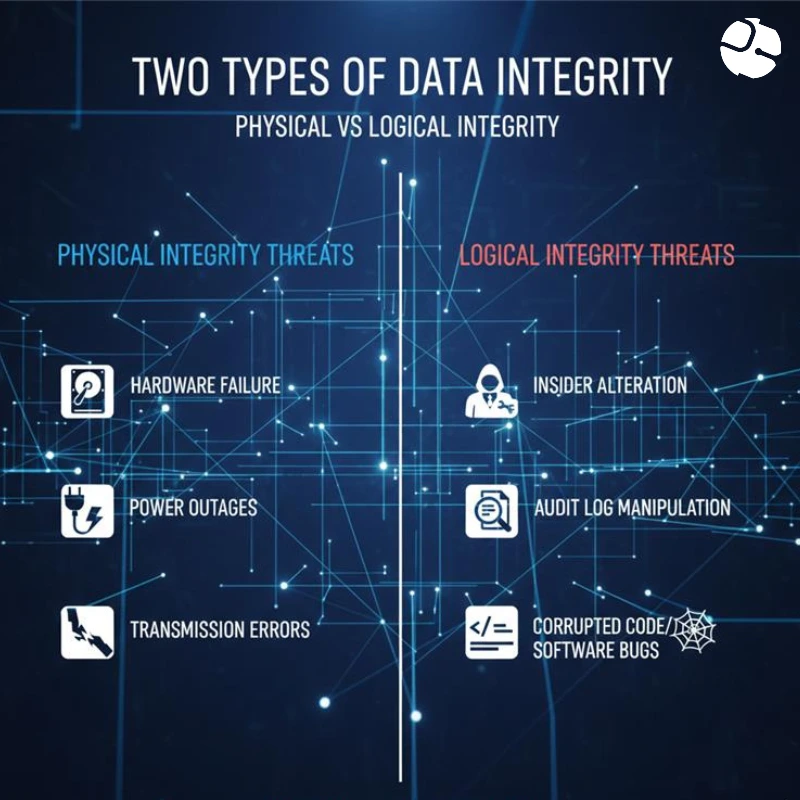
There are two types of Data Integrity
Most enterprises understand data integrity at only one level, completely missing out where the real danger lies.
1. Physical Integrity
This protects data from hardware failures and transmission errors. We’re talking about:
· Disk corruption from bit rot or physical damage
· Network errors during data transfer
· Power failures mid-transaction
Traditional IT has largely solved this challenge through backups, RAID configurations, checksums, and error-correcting codes. When someone says “we have data integrity covered,” they’re usually referring to physical integrity. And they’re right but most organizations have this half of the equation managed.
2. Logical Integrity
This is where enterprises are dangerously exposed. Logical integrity protects against unauthorized or undetectable logical changes to data. The threats here are far more insidious:
· A privileged database administrator altering financial records
· A hacker not stealing data, but subtly modifying transaction amounts
· An employee covering their tracks by editing audit logs
· Documents being changed without creating a verifiable history
Here’s the critical insight that keeps executives awake at night: You can have perfect physical integrity while suffering catastrophic logical integrity failures. Your backups work flawlessly, your hardware is redundant, your data transmission is error-free but you’re diligently backing up corrupted, manipulated, or falsified data. The enterprise threat isn’t losing your data; it’s discovering too late that you’ve been trusting data that was not accurate to begin with.
Why Logical Integrity is a Critical Issue
Logical failures don’t crash systems. They don’t trigger alarms. They don’t look dramatic. They’re quiet. They’re also:
· Hard to detect
· Easy to trust
· Quick to spread
· Difficult to prove
Once altered data enters reporting pipelines, analytics dashboards, and executive summaries, it becomes “fact.” Decisions get made. Money moves. Strategy shifts.
And later, if something feels off, proving what happened can be nearly impossible.
Why is Data Integrity Important for Enterprise Businesses?
Imagine discovering that your quarterly financial statements have been incorrect for the last three quarters. Not because of accounting errors, but because someone with database access altered revenue numbers. To add to this, you can’t determine:
· When the changes were made
· What the original numbers were
· Who made the alterations
Without cryptographic proof, you’re relying on logs stored in the same system that may have been altered. That’s a weak position in court. Or in front of regulators. And the costs aren’t abstract.
· Undetected fraud that compounds over time
· Supply chain breakdowns when inventory data doesn’t match warehouse reality
· Wasted resources chasing opportunities based on falsified market data
· Massive write-offs when financial discrepancies finally surface
In 2022, a National Retail Federation (NRF) survey reported that internal theft accounted for 29% of total annual inventory shrinkage. A sizeable chunk which was only reported after the fact and in most cases, entirely preventable had the underlying inventory records been tamper-proof and verifiable from the start.
The Compliance Nightmare
Regulations such as GDPR, HIPAA, SOX, and CCPA increasingly focus on more than perimeter security. It is no longer sufficient to restrict access to sensitive records. Organizations must also be able to demonstrate that records have remained accurate and unchanged over time.
That distinction becomes important during audits, regulatory reviews, or legal disputes. If audit logs sit inside the same system they are meant to monitor, questions naturally arise about their independence. When verification relies on the same database architecture that stores operational data, proving integrity can become complicated.
Many companies only recognize this gap when they are asked to produce defensible evidence and discover their systems were designed for storage and access not provability.
Risks of Running a Business on Corrupted Records
Most companies like to think they are data-driven. Budgets, expansion plans, pricing, operations all things which rely on dashboards and reports.
The problem is those systems assume the underlying data is accurate.
If records are incomplete, altered, or inconsistently updated, the mistakes go beyond reporting. Analytical tools, including AI models and forecasting systems, amplify errors. The more advanced your analytics, the bigger the impact.
For example, acquisition evaluations might be based on inaccurate financials. Expansion plans could follow skewed customer data. Research projects might use incomplete or altered datasets. Budgets might be tied to unreliable performance metrics.
The risk is not just technical. It is strategic.
Trust and Institutional Credibility
Data integrity failures hurt differently than typical security breaches. A breach usually means someone broke in from the outside. An integrity failure says your own systems cannot be relied on. That is harder to recover from.
When discrepancies appear, customers question whether their information is handled responsibly. Investors may doubt financial reporting. Partners might reconsider data-sharing relationships. Employees can lose faith in leadership.
Fixing this is not just a matter of updating systems. It often requires rethinking how information is recorded, verified, and audited.
The Human Impact of Data Integrity Failures
Nowhere is this clearer than healthcare. In under-resourced public systems, including parts of Bangladesh, weak data controls can cause serious harm.
Patients may be treated without full knowledge of prior diagnoses. Life-saving medications can be diverted because inventory records are altered. Complaints may disappear in the system, leaving issues unaddressed. Professional credentials might be insufficiently verified. Treatment records can be incomplete, making follow-up care difficult.
Data integrity is not just an IT issue. When records cannot be trusted, the consequences are real. They affect services, accountability, and public confidence.
Common Threats to Data Integrity
Most risks do not come from hackers in far-off countries. They come from inside the organization.
Privileged users, like database administrators and senior IT staff, have wide access. If they change data, they can cover their tracks. A well-known saying goes: “He who controls the database controls the truth.”
Human error is also a factor. Even small corrections can spread through billing, CRM, and analytics systems. Without records that cannot be overwritten, there is no simple way to revert mistakes.
Fraud happens more often than companies admit. Financial controllers, inventory managers, or HR staff might alter records for personal gain. In traditional systems, the audit trail is often stored in the same database, making it easy to hide manipulations.
External threats are evolving too. Hackers now target subtle data changes rather than obvious breaches. A single altered transaction or research record can divert funds or sabotage outcomes, often without leaving clear evidence.
Supply chain vulnerabilities add another layer. A partner or supplier with bad data can pass it on, and tracing it back is nearly impossible.
AI-powered attacks are an emerging threat. They can adjust data in ways that look normal statistically but fundamentally change results. Traditional tools often do not detect these alterations.
Why Centralized Databases Create a Single Point of Failure
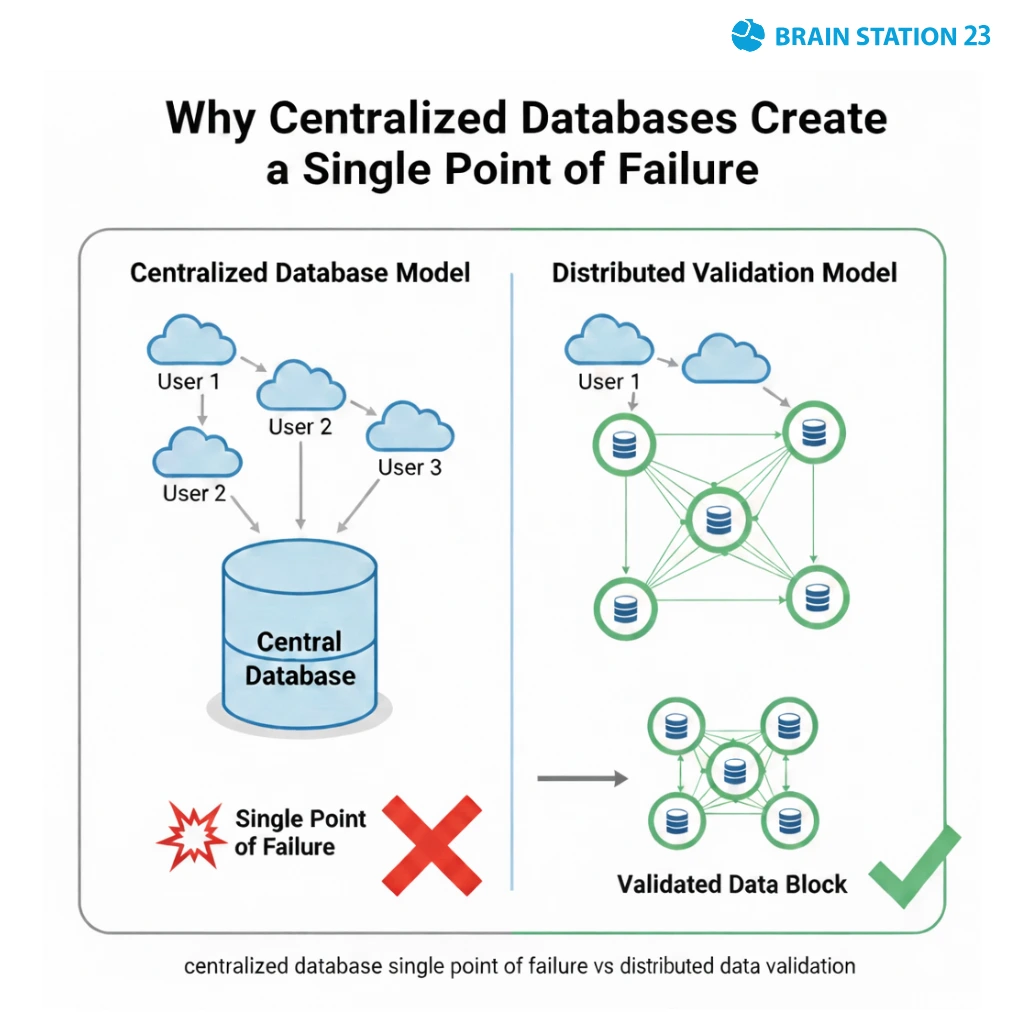
Many enterprises rely on a single centralized database as their source of truth. This works until it fails.
If that database is compromised, every system that depends on it inherits the error. Reports, dashboards, integrations, and partner feeds all become unreliable.
Audit logs do not fully solve the problem. They are often editable by the same administrators. Asking a system to verify its own data is circular logic.
Modern ecosystems add more complexity. Data moves constantly between CRM, ERP, analytics platforms, and cloud services. Each transfer carries risk. By the time corruption is noticed, figuring out the source can feel impossible.
Can Your Organization Prove Its Records Haven't Been Tampered With?
Ask your IT leadership:
If a critical record changed tomorrow, could we prove that it was altered? Could we identify the original value? Could we know who made the change and when? Could we confirm that no other records were affected at the same time?
If the answer relies on trusting logs or administrators, you do not have provable integrity. You have hope. Hope is not enough.
Why Access Controls and Audit Logs Give a False Sense of Security
Many companies still rely on tools designed for the internet of 2005. Permissions, audits, backups. These measures create an illusion of safety.
Access controls stop outsiders but do nothing if a trusted insider changes data. Database rules catch obvious errors, but not well-planned manipulations. Periodic audits are slow. By the time you spot a problem, the damage is already done. Audit logs stored alongside the data are not reliable. Backups only help if you know exactly when the corruption happened. Otherwise, you are just saving a copy of the same bad data.
What Modern Data Integrity Requires
Forward-thinking companies are moving beyond trust. They focus on three things.
First, records that cannot be quietly erased. Old data stays while new versions are added. Overwriting is not allowed. This matters for financial transactions, medical records, and legal documents.
Second, proof anyone can check. Auditors, regulators, or customers should be able to verify data authenticity themselves without special tools.
Third, certainty about actions. Not just the system’s claim that a user made a change, but cryptographic proof that they did. Timestamps must be reliable. Chains of custody need to survive personnel changes or system upgrades.
How Enterprise Blockchain Architecture Ensures Data Integrity
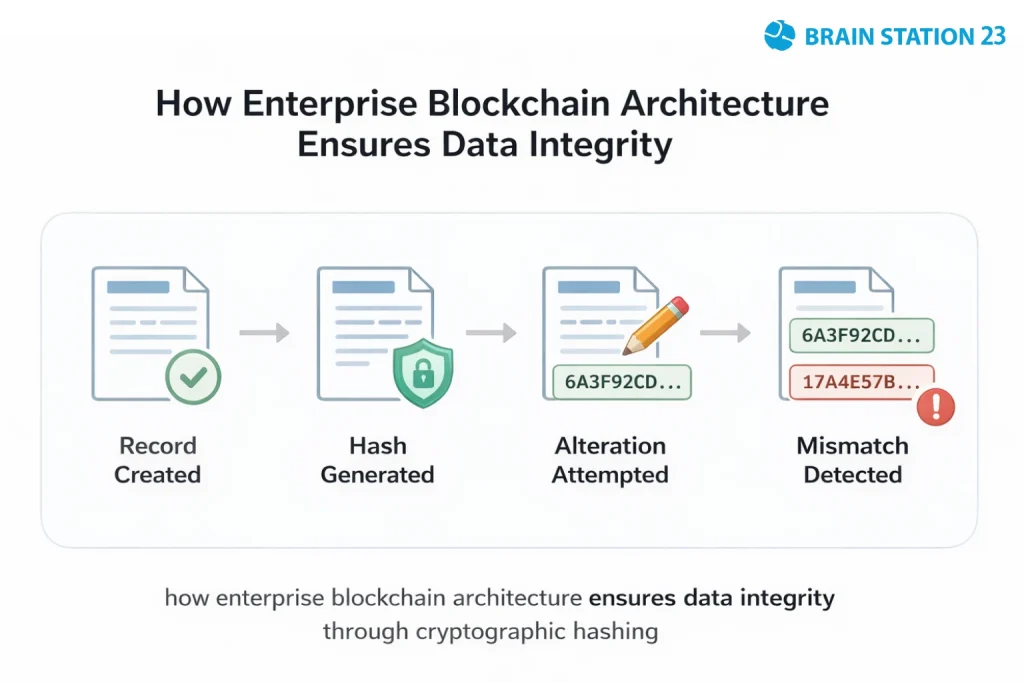
More companies are starting to question whether access controls and internal audits are enough to prove that data has not been changed. This is where enterprise blockchain architecture is getting attention. When a record is created, it is cryptographically hashed. If someone alters it later, the hash changes and that mismatch signals a problem. Unlike traditional databases where records can be quietly overwritten, a blockchain audit trail keeps the full history intact.
Through private blockchain development, organizations control who participates in validation without exposing sensitive data to public networks. Multiple authorized nodes confirm transactions before they are finalized, reducing the risk of undetected insider manipulation. A privacy-preserving enterprise blockchain allows companies to encrypt fields and restrict access while still maintaining verifiable, tamper-evident records.
Enterprise blockchain development services make this practical by integrating blockchain layers with existing databases, compliance workflows, and reporting tools. The goal is to make integrity part of the foundation rather than something investigated after problems surface. Organizations increasingly need systems that can prove reliability, not just claim it.
Data Integrity Is the Foundation Everything Else Is Built On
Every business decision, compliance obligation, and stakeholder relationship rests on one assumption, that your data can be trusted. The threat is not always a dramatic breach or a system failure. More often it is a quiet, undetected alteration that compounds silently until the damage is too large to ignore.
When that foundation cracks, everything built on top of it becomes questionable. Organizations that treat data integrity as provable rather than assumed are the ones that will maintain trust, withstand regulatory scrutiny, and make decisions they can stand behind. The question was never whether your data is stored safely. It is whether you can prove it has never been touched.
